Thanks to its flexibility and simplicity, Ruby is an extremely popular programming language, used for a variety of applications from web development to data analysis.
Central to the Ruby ecosystem is Rack, a modular interface that connects web servers to Ruby-based web applications which is used by many Ruby web frameworks and libraries, such as Ruby on Rails, and Sinatra.
However, the security of web applications, such as those created through Ruby Rack, can be compromised by hackers' intent on finding and exploiting vulnerabilities. This can leave organizations open to attacks and at risk of data loss, data theft and the resulting legal, financial, and reputational implications.
Find out how OPSWAT's Red Team uncovered vulnerabilities impacting the Rack framework and collaborated closely with Ruby’s developers to quickly fix them.
Apa Masalahnya?
Ruby Rack is a core component of many web applications used by businesses and consumers. Flaws or vulnerabilities in Rack pose significant security risks to Ruby-based web applications. This could allow an attacker to:
- Gain unauthorized access to files
- Manipulate log content and log entries in Ruby
Why Does This Matter?
With more than one billion downloads of Rack globally, the exploitation of vulnerabilities within Rack could potentially affect many applications and systems worldwide.
The Bugs Discovered: What You Need to Know
1. CVE-2025-27610 (CVSS score of 7.5)
The most severe vulnerability out of the three discovered is a Path Traversal vulnerability that occurs due to the improper handling of the :root option, which defines the base directory from which the static files will be served. By enabling attackers to gain access to files located outside the designated static file directory and retrieve sensitive information, including configuration files, credentials, and confidential data, it can lead to a breach.
2. CVE-2025-27111 (CVSS score of 6.9)
This security flaw allows attackers to inject and manipulate log content through malicious header values. Attackers could insert fraudulent entries, potentially obscuring real activity, or inject malicious data into log files.
3. CVE-2025-25184 (CVSS score of 5.4)
This vulnerability enables attackers to perform log injections via CRLF (Carriage Return Line Feed) characters, potentially manipulating log entries, masking real activity, or inserting malicious data into log files.
Apa yang Harus Dilakukan oleh Para Pengembang?
1. Update Ruby Rack Now
Ruby has fixed the bugs in the newest versions of their software. If you are using Rack, update it immediately to the latest version.
2. Audit Your Web Frameworks
Developers should scan their Software Bill of Materials (SBOM)—a list of all the tools and code they use—to make sure nothing else contains any bugs.
An SBOM provides visibility into the components and dependencies that make up software, so security teams can quickly identify and address any vulnerabilities. In modern web development, the use of multiple software tools and third-party libraries significantly increases the complexity of environments, making it challenging to maintain a software development lifecycle (SDLC).
Without continuous monitoring of the SBOM, organizations offer a chance for attackers to exploit their outdated or vulnerable components, leaving their applications and data at risk. Proactive SBOM scanning helps streamline vulnerability management, ensuring that security remains an integral part of the SDLC.
3. Protect Your Data
Hackers can exploit these vulnerabilities to alter log contents and files. Web frameworks, even if initially secure, may not remain so over time. Regularly scanning web frameworks for changes or vulnerabilities helps maintain security and tools such as sandboxing and file scanning are effective in identifying suspicious activities.
OPSWAT’s MetaDefender Core enables organizations to take a proactive approach in addressing security risks. By scanning software applications and their dependencies, MetaDefender Core identifies known vulnerabilities, such as CVE-2025-27610, CVE-2025-27111 and CVE-2025-25184, within the listed components. This empowers development and security teams to prioritize patching efforts, mitigating potential security risks before they can be exploited by malicious actors.
Bagaimana Kami Dapat Membantu?
OPSWAT mengkhususkan diri dalam teknologi dan solusi yang mendeteksi malware dan bug semacam ini, sehingga membantu perusahaan tetap aman. Jika Anda seorang pengembang, kami dapat membantu Anda memindai aplikasi dan data Anda untuk mendeteksi risiko, memastikan alat-alat Anda selalu diperbarui, serta melindungi informasi Anda dari peretas.
Poin Utama
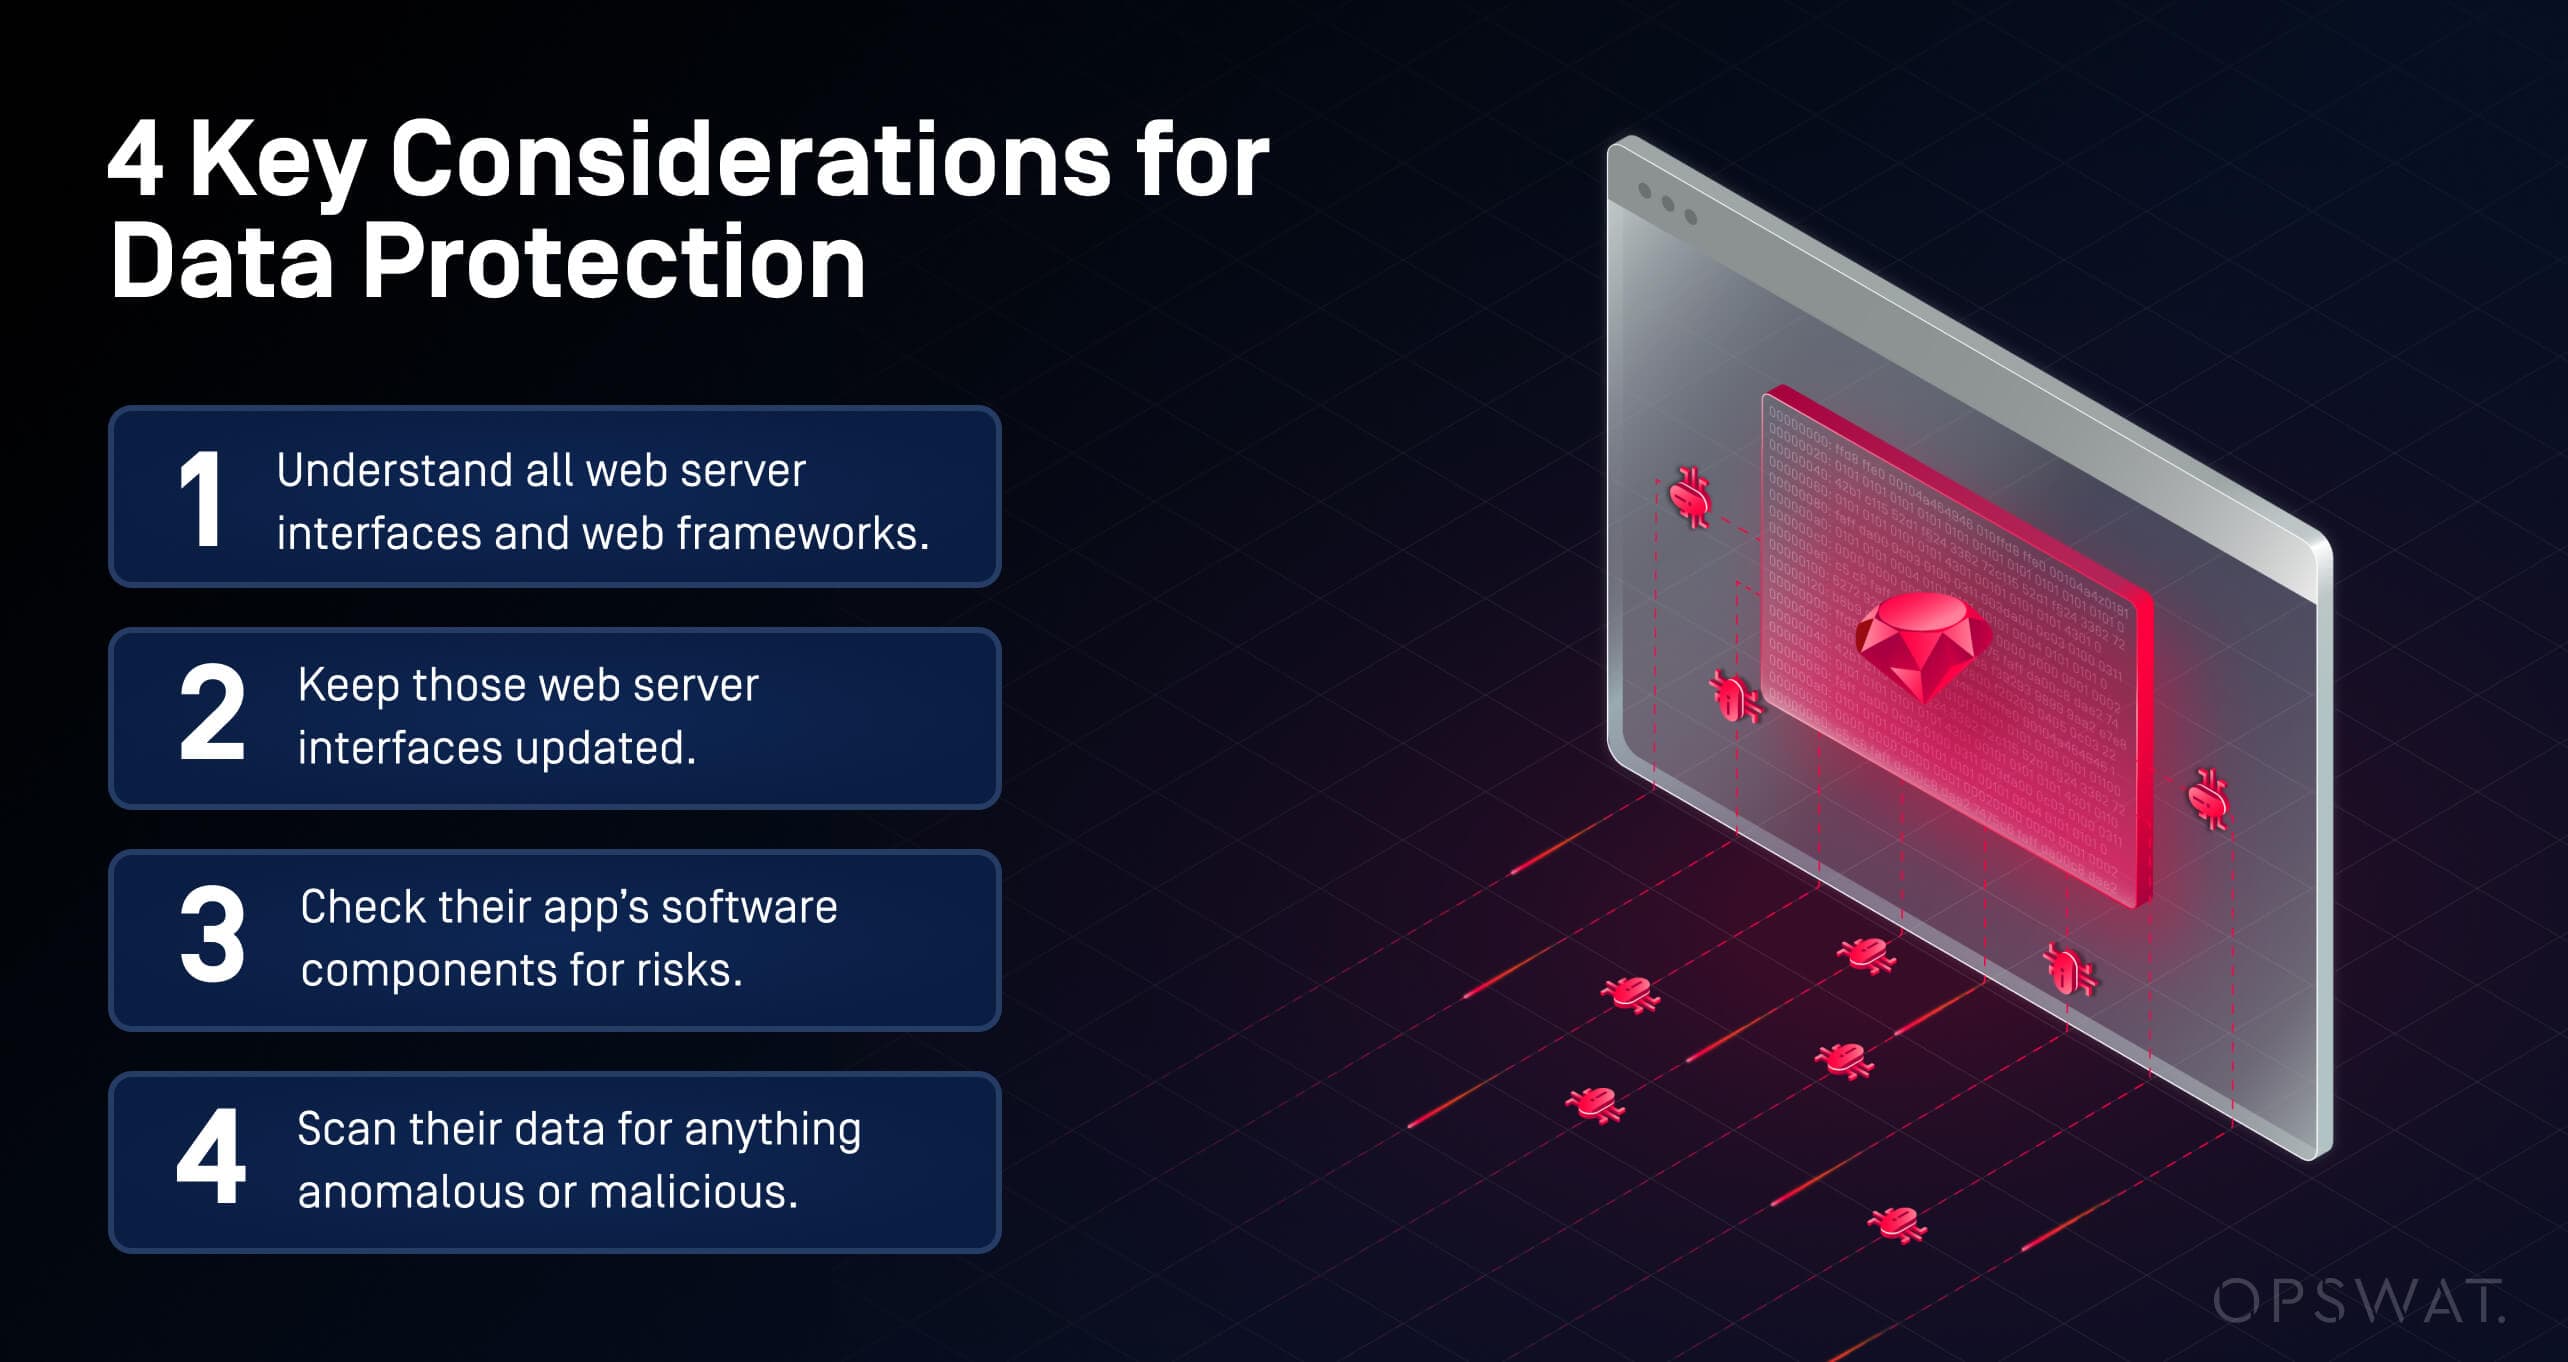
Bugs in web server interfaces like Rack can have a significant impact if hackers find and use them first. Developers need to focus on four key items to stay ahead:
- Understand all web server interfaces and web frameworks used in their software builds.
- Keep those web server interfaces updated.
- Periksa komponen perangkat lunak aplikasi mereka untuk mengidentifikasi risiko.
- Periksa data mereka untuk mendeteksi hal-hal yang tidak wajar atau berbahaya.
Memperkuat Budaya Keamanan Siber
Want to learn more about how OPSWAT’s Red Team discovered—and helped patch—these CVEs? Get all the details and read about how the program is contributing to the global cybersecurity community.
Jika Anda seorang pengembang atau pemilik bisnis, sekaranglah saatnya untuk memastikan bahwa aplikasi dan data Anda terlindungi.
Whether it’s SBOM or the multilayered threat detection and prevention found in MetaDefender Core, our experts are ready to show you why OPSWAT is trusted globally to defend some of the most critical environments from threats.
Ingin mengetahui bagaimana OPSWAT dapat melindungi lingkungan Anda dari ancaman yang muncul?